Velenza BOC
The audit is already done.
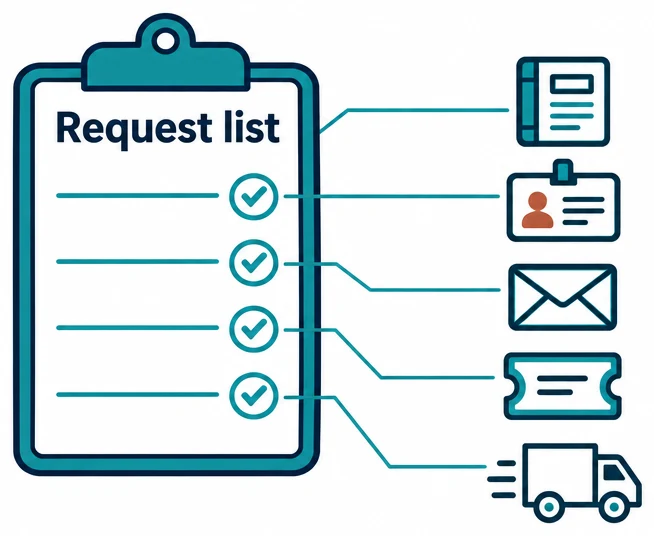
Every audit starts with a request list. Yours is already answered.
A financial audit, a DOT safety review, a SOC 2 security exam, a workers’ comp premium audit, a customer’s security questionnaire: each one turns the company into a scavenger hunt through accounting, HR, email, tickets, dispatch and people’s memories. Velenza keeps every figure linked to the record behind it, and every approval and conversation in context. The proof exists before anyone asks.
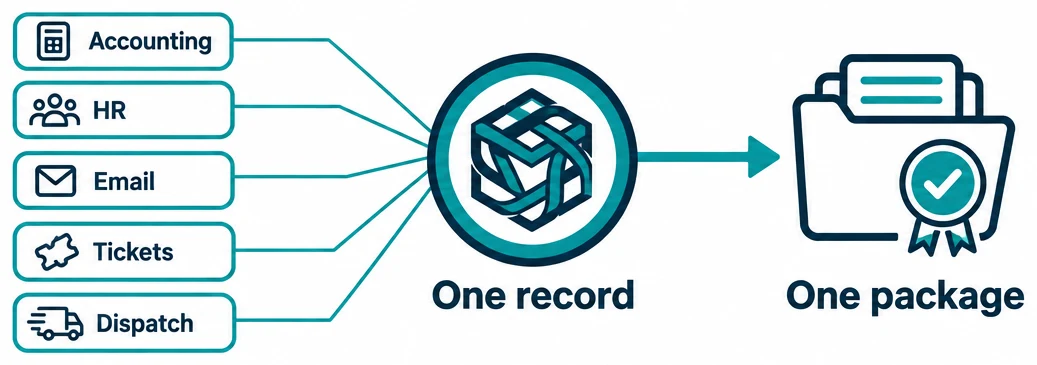
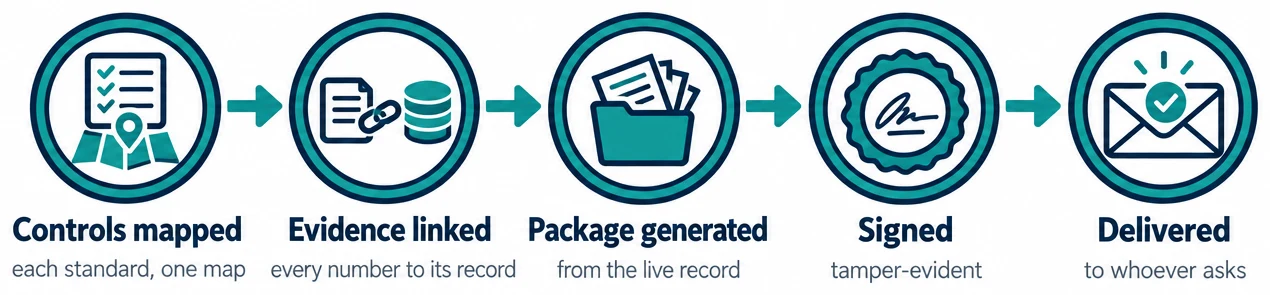
The evidence is already linkedEvery number traces to its source record. Every approval, review and meeting is attached to the thing it changed.
One click, one packageA compliance module maps a standard’s controls to those links and generates the documentation an auditor asks for, from the live record, signed.
Watched between auditsThe CLO, CISO and CFO seats read the record every day and raise what is slipping the week it starts, not the week the auditor arrives.
What the scramble costs
The company usually did the right thing. It cannot show it quickly. Auditors rarely fail a company for lacking controls; they fail it for lacking proof that the controls ran.
of staff time a year spent on compliance tasks.
of SOC 2 security exams carry at least one exception, most for missing proof that a control ran.
average back wages per worker recovered by the U.S. Department of Labor in FY2025, 177,000 workers.
With Velenza the request list is a question, not a project.
Where today’s tools stop
Compliance platforms collect evidence from cloud and login systems. The HR ticket for a departure, the board minute, the signed rate confirmation, the email approval and the maintenance invoice stay manual, so the auditor’s request list is answered by people. Velenza answers it from the record.
You did the right thing. Now you can show it in an hour.
Velenza BOC
How audit on demand works.
The examiner asks: show that every employee who left in Q2 lost access within 24 hours.
VelenzaFourteen departures in Q2 (HR). Fourteen access removals, median three hours (login system), each linked to its HR ticket. One exception, a contractor removed at 31 hours: the CISO seat flagged it on 14 May and the fix is on the record.
The DOT investigator asks: driver qualification files for every driver employed in the period.
VelenzaFifty-two drivers, fifty-two files. Medical certificates current. Two annual reviews due within 30 days, already queued with the safety manager.
Illustrative exchanges. The figures are examples.
In the room: CLO · Oliver Wendell Holmes Jr., CISO · Sun Tzu, CFO · Luca Pacioli
Built in, not bolted on
Compliance modulesEach standard (SOC 2, ISO 27001, DOT, wage-and-hour, insurance) is a map from its controls to the records that prove them. Add a module; the package follows.
Signed, not sampledEvery entry in the package carries its signature and its source, so an auditor can verify the record itself instead of sampling last quarter’s controls.
Seen earlyExpiring certificates, overdue reviews and missing approvals surface to the seat that owns them while there is still time to fix them.
One package, every audience
The same question, in different wordsThe financial auditor, the DOT investigator, the SOC 2 examiner, the wage-and-hour inspector, your enterprise customer’s security team and your insurer at renewal all ask: prove it. Each gets the same record, limited to what it is entitled to see.
The insurer is an auditor tooUnderwriters price what they cannot see. Trucking insurance premiums rose 3.9% in 2025 (ATRI); cyber renewals ask for proof of two-factor login, backups and endpoint protection. The same package answers the underwriter.
Worked examples and industry figures, never a measured result; your figures come from your record.
Where else it applies
Manufacturing (ISO 9001, OSHA, CMMC), healthcare practices (HIPAA, payer audits), construction (certified payroll, licensing), any company with a lender, a regulator or an enterprise customer.
Where this case ends
This case proves to an outsider that the controls operated. Loss and fraud in the gaps is about catching what the controls missed.
Take back control of your business
Velenza sits above your existing platforms and connects their records and conversations. Keep what works; choose native capabilities on your terms.
Brandon Meyer | Founder/CEO, Velenza BOC Inc
brandon@velenzaboc.com | www.velenzaboc.com